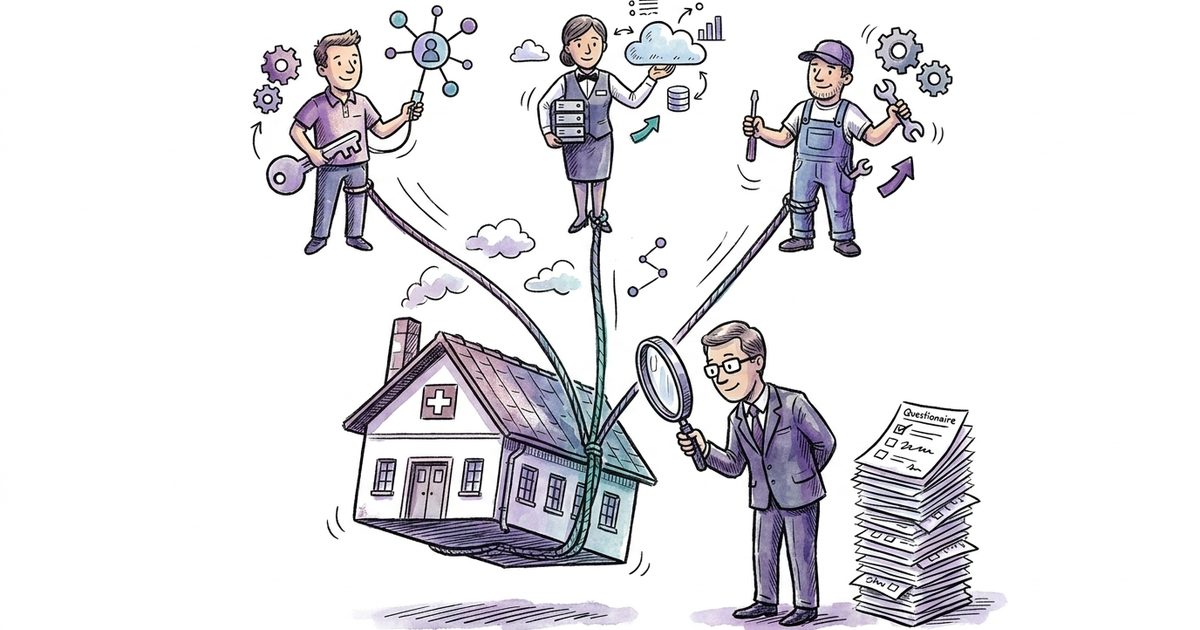
The cyberattack that stops your company does not have to happen on your premises. When your IT provider gets encrypted, your systems stand still, even if your own firewall did everything right. That is the core of supplier risk: with every contract, you buy the provider's security posture along with the service. Every SME has dependencies like these. The difference lies in whether you know which of them can stop your business.
What is supplier risk and why does it hit SMEs particularly hard?
Supplier risk is the risk that a security incident at a supplier hits your own business: through remote access to your systems, through compromised software or through the outage of a service your operations depend on. It hits SMEs particularly hard because they outsource more than large companies and at the same time have less negotiating power to enforce security requirements.
A company with 50 to 500 employees rarely runs everything itself. IT runs partly or fully at a service provider, the ERP at a hoster, payroll at a fiduciary, and the production machines hang on the manufacturer's remote maintenance. Each of these relationships makes commercial sense. Taken together, they form an attack surface that is visible in none of your own systems.
Responsibility still stays with you. Your customers do not care whether the failure happened at your site or at your hoster's; their contract is with you. You can outsource work, not responsibility.
The Swiss Federal Office for Cybersecurity BACS has dedicated its own guidance to the topic: Cybersicherheit in der Lieferkette describes a cycle of understanding dependencies, categorising suppliers, setting requirements and verifying them. The approach is remarkably calm: no certificate mandate for everyone, but first the question of where you actually depend on someone.
Why questionnaires for everyone protect no one
The standard reflex in supplier management is the questionnaire. Forty questions to every supplier, once a year, answers filed, box ticked. It feels like control and produces one thing above all: paper. Large companies can afford this ritual, they have teams for it. An SME that copies it gets the form without the effect.
Let's be honest: what happens with the answers? In most companies, nobody who could draw consequences ever reads them. The supplier who would tick No next to "password policy in place?" does not exist. And the supplier who can endanger you does not stand out in a questionnaire, because the danger sits not in his answers but in your dependency on him.
The question that appears on no form: what do you do on Monday if this supplier got encrypted on Friday? If the answer is "no idea", no completed questionnaire in the world will help you.
Supplier risk is also a right-sizing problem. More questionnaires do not make you safer, sharper ones do: a few critical suppliers you understand in detail, instead of complete files on everyone. More protection, less effort.
Which suppliers do you have to check?
Three groups: suppliers with privileged access to your systems, operators of your core systems, and manufacturers of software or hardware in critical processes. In its guidance, BACS recommends exactly this categorisation by risk rather than by purchasing volume. In our experience, out of a few hundred creditors, ten to twenty suppliers remain that meet one of these criteria.
What that looks like in practice: a Swiss industrial company with around 120 employees we worked with carried over 300 creditors. Procurement checked the 30 largest by purchasing volume, among them the coffee supplier and the building cleaner. Not on the list: the external IT provider with domain admin rights, the ERP hoster and the machine builder with permanent remote maintenance access. The three firms that could have stopped operations in an afternoon had never been looked at, because they were inconspicuous in procurement. The new list ended up with twelve names. Three of them led to conversations and adjusted contracts, the rest were covered with evidence and standard clauses. The effort: a few working days spread over a quarter, with no new tool and no new position.
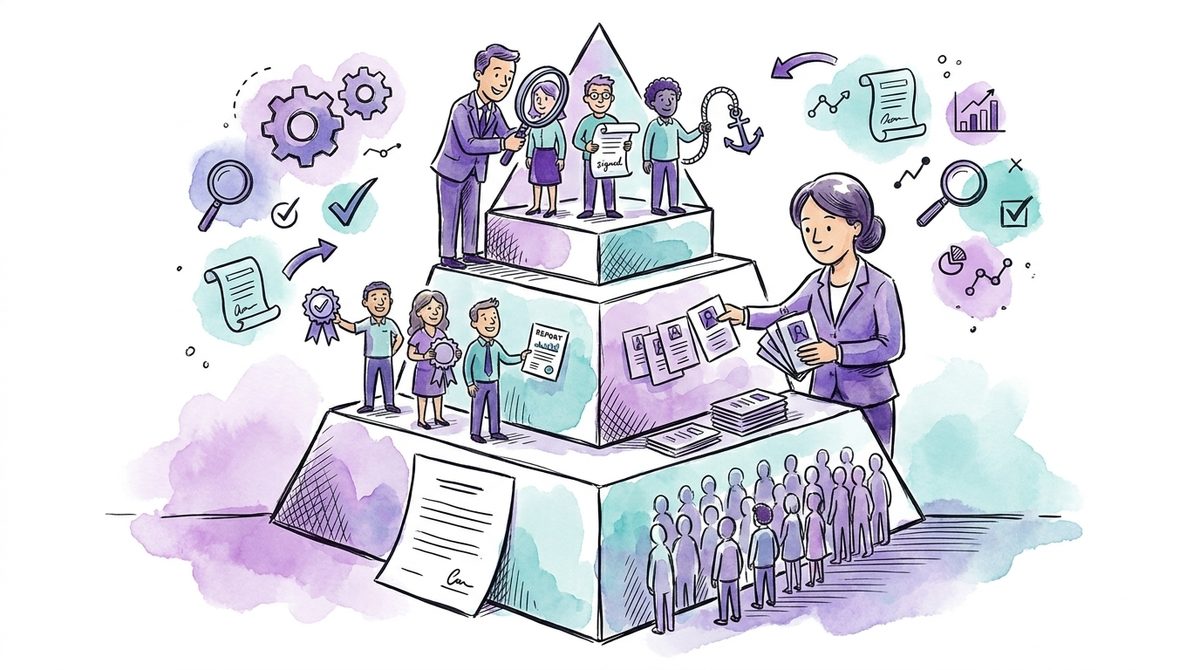
The list therefore comes not from procurement but from a conversation with operations: which systems must not stand still, who has access, which software sits in which process. A usable supplier register ends up with three tiers. Critical suppliers get a deeper review, clear contracts and a plan B. Elevated ones get evidence and reporting duties. The rest get standard clauses in procurement. This sorting is manageable effort and holds for years.
What can an SME demand from suppliers at all?
Less than you would like, and more than you think. Microsoft will not answer your questionnaire, your local IT provider will, and the actual work lies in between: deciding per supplier which evidence is realistic and which contract point counts.
With the big ones, it runs on existing evidence. Hyperscalers and established software vendors publish certificates and audit reports, above all ISO 27001 and SOC 2. Your job there: read the answers that already exist, including the scope. Which proof says what, we have written up in our comparison of ISO 27001 and SOC 2.
With the small ones, and these are often the most critical, dialogue works better than audit theatre. Your IT provider with 15 people has no SOC 2 report and will not have one any time soon. A conversation about how he protects his own admin access says more than 40 form fields. BACS argues in the same direction: enable suppliers rather than punish them, because a secure supplier is worth more to you than a caught one.
In the contract, few points count: that the supplier reports security incidents to you within a defined deadline, that he discloses subcontractors, that your data comes back at the end of the contract and that you get information when it matters. These clauses cost almost nothing in negotiation as long as the contract is not yet signed. Afterwards they cost a lot.
Concentration risk: when there is no plan B
The hardest form of supplier risk is not the insecure supplier but the irreplaceable one. If your ERP hoster, your industry software or your IT provider fails tomorrow or doubles its prices and you have no realistic alternative, your operations stand just as still as after an attack. Vendor lock-in is supplier risk in its purest form, only without an attacker. What leaving costs in practice and how to keep the exit contractually open is covered further down, in the section on vendor lock-in.
A plan B in an SME does not mean running every system twice. That would be the expensive answer to the wrong question. It means knowing the exit costs before they fall due. Is your data available in a format another provider can read? Does the contract say you get it back in full on termination, and within what deadline? Is there a second provider who could in principle deliver the most critical service, even if the switch would take months? Whoever can answer these questions negotiates differently. Not because he threatens, but because both sides know that he could.
A board that asks for the biggest risks often gets a list with malware and phishing. In many SMEs the more honest answer would be: the one service provider without whom nothing runs any more.
At the latest here, supplier risk turns from an IT task into a management task. The decision to enter a dependency deliberately, because the provider is plainly the best, can be right. It just should not happen by accident, because nobody asked the question.
Vendor lock-in does not come from the contract, it comes from operations
Nobody signs a clause forbidding a switch. The company slides into it, over years, through a series of sensible individual decisions.
- The privileged accounts belong to the provider. His team has its own administrators in your directory, your own people have standard rights. Convenient, until you want to let somebody else in.
- The licences run through his contract. You are a user, not a contracting party. In a switch the contracts move, and the identities underneath them move with them.
- The documentation is his documentation. Network diagram, firewall rules, the justification for that exception from 2021: complete, and out of your reach.
- The knowledge has two names, and both are on his payroll. Those two people know your environment better than any document does.
- The backups sit in his infrastructure. The restore works as long as he runs the tooling for it.
None of this is bad faith. Every single point is convenient, and convenience is the route by which dependency enters the building. That a provider runs your security without leading it is a topic of its own, which we took apart in Security and your IT provider.
FINMA, the Swiss financial market supervisory authority, observes the same mechanism in a regulated industry and describes it unusually plainly: financial institutions are becoming increasingly dependent on service providers for important functions, and the supervisor sees an elevated concentration among individual providers, because the same firms deliver critical functions for many institutions (FINMA on cyber risks and outsourcing). Most SMEs are not supervised. The mechanism does not know the difference.
The usual answer to dependency is called second source: two providers for everything that matters. In a company of this size that doubles the contracts and the coordination effort, and halves the attention paid to either side. What makes you independent is not a second supplier, it is the ability to take on a new one within a reasonable time. More protection, fewer contracts, lower cost.
How do you know you can no longer switch?
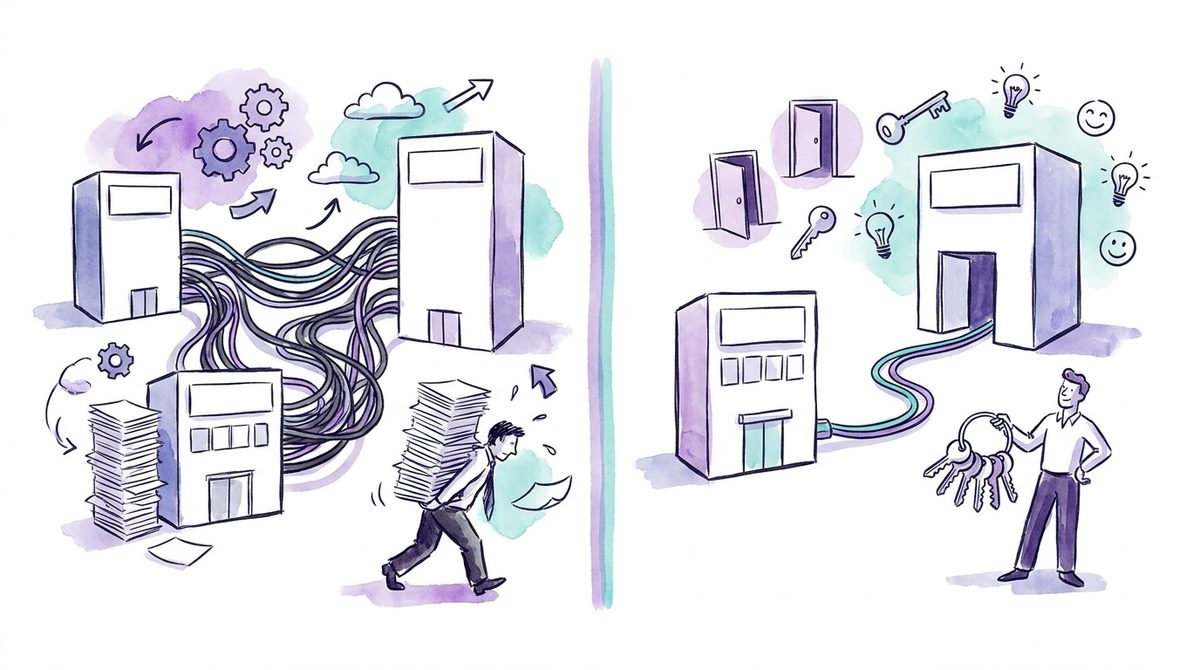
Three questions are enough. Who in your company can create an administrator today without the provider? How long does it take to obtain the complete system documentation if he does not cooperate? And how many weeks would a change of provider weigh on operations? If the answers are nobody, unclear and no idea, the price is no longer negotiable.
The most honest indicator is already sitting in your accounts. If the last price increase went through without discussion, the company has already given up its position, whatever the contract allows for. That is not a question of blame. It is a status report.
Let us be honest: in many companies the answer to all three questions is uncomfortable. That is the normal case and not the exception. All that counts is that somebody in the company asks them before the provider does.
What exit capability looks like day to day
Exit capability has no end date. It is a condition a company either holds or loses, and four things carry it. All four are organisational, none of them technical.
| What stays in house | Why it gives you back negotiating power |
|---|---|
| Identities and contracts | The provider works with rights you delegated to him and can withdraw again. This is the only point at which a termination becomes technically enforceable. Everything else is wording. |
| Current documentation | If the state of the environment regularly lands with you, nobody holds knowledge as collateral. The side effect is immediate: anyone who has to document works more cleanly. |
| Readable data formats | Whether you get your data out depends on the format and not on goodwill. What only opens with his software effectively belongs to him. |
| The switching cost as a number | A rough estimate in months and francs is enough, as long as your management team knows it and it is not from 2019. |
The benefit shows up long before any switch, namely in the conversation about it. An SLA you cannot enforce is a statement of intent. It becomes enforceable the moment both sides know that a switch would be possible. That is the whole lever, and it has nothing to do with security technology.
BACS, the Swiss federal office for cyber security, is very clear at one point in its recommendations for working with IT providers: accountability cannot be outsourced or delegated. Alongside that, the recommendations name liability in the event of damage, tested restores and periodic security audits as points to settle contractually. Many SME contracts do not contain this, rarely out of negligence, mostly because the contracts date from a time when the IT estate was smaller and the provider was not yet half inside operations.
When does a second supplier pay off?
Rarely, and only where standstill costs more than running two tracks for a year. The sum is unspectacular: what two days without this service cost, how likely a failure is within a year, and what the second contract charges for it. For internet connectivity and links between sites it often adds up. For the IT service provider itself, almost never.
The reason is not only money. Two providers for the same environment mean two levels of knowledge, two escalation paths and a new favourite answer when something breaks: that was the other one. In our experience that costs companies of this size more than the outage it is meant to prevent.
What holds up is a split. For the two or three services where standstill costs revenue directly, you need a named plan B that does not hang off the same provider. For everything else, exit capability is enough. It is the same sizing question as with tools: what do you need twice, and what do you only need to have under control?
How the ISG, NIS2 and DORA put the topic on your desk
The regulation does not target you, but it arrives at your door. The Swiss Information Security Act (ISG) obliges operators of critical infrastructures: since April 2025 a reporting duty for cyberattacks within 24 hours applies, and by the end of 2026 organisations subject to the act need a working ISMS. Those affected pass these requirements on to their suppliers by contract. NIS2 does the same from the EU side, and we have described separately how the rule arrives in Switzerland through customer contracts. DORA does it for suppliers of EU financial institutions.
Which also means: if your customers are regulated, you are their supplier risk. The same sort of questionnaire you send to your suppliers lands on your desk from the other side. Whoever has their own supplier management under control answers these questions more credibly. A compliance exercise turns into a sales argument.
Supplier risk remains part of ongoing security leadership: the list lives, access and contracts change. That is why, for us, the topic belongs in ongoing security leadership on a mandate rather than in a yearly project. Whether that adds up for your company, one conversation settles faster than yet another questionnaire.
Frequently asked questions
Is a supplier's ISO 27001 certificate enough as evidence?
It is a good filter, not a guarantee. The certificate proves a working management system within the defined scope. Whether the service you are buying sits inside that scope is written in the scope statement, and almost nobody reads it. Certificate plus matching scope plus a contractual reporting duty is a solid basis.
How often should you reassess suppliers?
Event-driven beats calendar-driven. You look at critical suppliers again when something changes: a new subcontractor, new access, an acquisition, a publicly known incident. An annual review of the critical list is enough of a rhythm, as long as these triggers are defined. A rigid yearly ritual for all 300 creditors keeps you busy without protecting you.
Does an SME need a dedicated tool for supplier risk?
In most cases no. Ten to twenty critical suppliers fit into a table in your existing risk register. Tools pay off when hundreds of suppliers with continuously updated ratings need managing, which is rare below corporate scale. First the process, then the question of tooling.
What if the provider does not cooperate with the disentangling?
Then you know more about the relationship than any questionnaire could show you. Reputable providers have no problem supplying documentation and holding administrator rights by delegation rather than by possession, because it does not threaten their business. Resistance at this point is itself the answer to the question of whether a switch should be examined.
Does this apply to the large cloud providers too?
With a large cloud provider the question looks different. The issue there is less the outage than the move: data sits in formats and services that make a switch expensive, and an SME has little negotiating power there. So the question belongs in the decision on the platform and not in the renewal. With a regional provider it is the other way round. There a switch is possible, it is just that nobody ever prepared one.