On 1 October 2026 Austria's NISG 2026 enters into force. It was promulgated back on 23 December 2025, and the nine months in between were the preparation window. For many companies it was mostly a waiting window.
The part that hits the leadership level directly rarely sits at the centre of the discussion. Governing bodies have to attend cybersecurity training designed specifically for them. A general IT briefing for all staff does not satisfy that.
What the law asks of governing bodies
The NISG 2026 follows the same logic as the NIS2 directive in the other EU states. Leadership is responsible for risk management measures being implemented and overseen, and it has to qualify itself for that job.
This is more than a formality. It is the answer to a pattern you see in every second incident: the technical issue was known, the risk was described internally, and the decision about it never landed in the right place.
Who counts as a governing body follows the legal form: managing directors, board members, managing partners. The head of IT does not, even though he or she knows the content better.
No deadline, still urgent
Registration comes with clear deadlines. For the training of governing bodies the law names no cut-off date. That regularly leads to the wrong conclusion, that it can wait.
The duty applies from the date the law takes effect. No cut-off does not mean later, it means from now on and without a grace period. And because a missing training record counts among the organisational breaches that can be penalised on their own, it is a topic even without an incident.
For organisational breaches, which include missing registration, late notifications and missing training records, fines of up to EUR 50,000 are provided for, and up to EUR 100,000 for repeat offences. For the entity itself the large frame applies: up to EUR 10 million or 2 percent of worldwide annual turnover for essential entities, up to EUR 7 million or 1.4 percent for important ones.
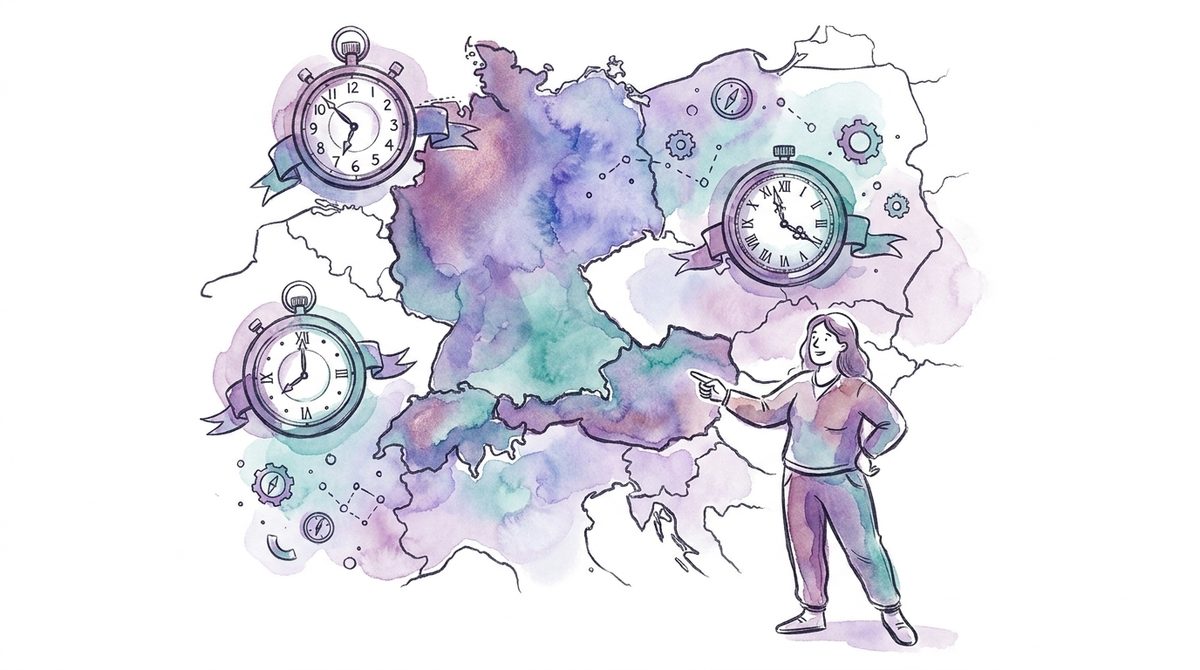
Three countries, three clocks
For Austrian companies with entities in Germany or Switzerland this gets messy, not because of the content, but because of the timelines.
- Germany: BSIG in force since 6 December 2025, training duty for management in Sec. 38 (3).
- Austria: NISG 2026 in force from 1 October 2026, training duty for governing bodies with no cut-off date.
- Switzerland: no NIS2. Instead, reporting and ISMS duties under the Information Security Act for critical infrastructure, and no training duty for leadership.
Inside one group that produces three different answers to the same question. Keeping it straight takes a register of entities with location, sector, size and the resulting classification. Without that register, every statement about being in scope is a guess.
What a session has to deliver to count
"Designed specifically" is the decisive phrase in the Austrian text. The measure is not whether somebody attended, but whether leadership can do its job afterwards.
Concretely that means three abilities: identify and assess risks, judge measures, estimate impact. All at the level where governing bodies actually work, so business processes, customers, contracts and budgets, not firewall rules.
And it means documentation. Participants with their roles, date, duration, content. The record is the part that counts in an incident, and it is easiest to produce on the day of the training itself.
What makes sense now
There is little time left before 1 October, and the duty runs from then. The pragmatic order:
- Clarify and document the classification, essential or important, per entity
- Prepare the registration so the formal part does not end up last
- Book a date for the leadership session before autumn fills up
- Decide where the training documentation lives and who maintains it
The effort for it is modest: an afternoon of preparation, half a day of delivery. What gets expensive is what follows, the measures themselves.
For groups we cover the differences between Austria, Germany and Switzerland in one sitting, in German or English: NIS2 training for executive management. What the German side requires in detail is in our article on the training duty under Sec. 38 BSIG.
Frequently asked questions
When does Austria's NISG 2026 apply?
The NISG 2026 was promulgated on 23 December 2025 and enters into force on 1 October 2026. For training governing bodies the law names no separate cut-off date, so the duty applies from the moment it takes effect.
Who counts as a governing body?
That follows the legal form: managing directors, board members and managing partners. The head of IT or the information security officer do not, even though they know the content better.
What are the penalties for missing training records?
Organisational breaches such as missing registration, late notifications or missing training records carry fines of up to EUR 50,000, and up to EUR 100,000 for repeat offences. For the entity itself the frame goes up to EUR 10 million or 2 percent of annual turnover.